Outsourcing your IT operations can reduce costs and free your team to focus on core business priorities. But handing off managed IT to a third-party vendor introduces risks that go far beyond the surface, especially in regulated industries like healthcare, finance, or manufacturing.
Cyber Advisors helps enterprises identify and address these managed IT outsourcing risks before they escalate into operational, financial, or compliance failures.
Let's dive deep into the key risks you should evaluate before signing an outsourcing agreement, and what you can do to protect your business at every stage.
Key Takeaways: Risks in Enterprise Managed IT Outsourcing
- Data security gaps from third-party access can expose sensitive records and trigger costly regulatory penalties.
- Loss of operational control makes it harder to enforce internal policies and meet compliance deadlines.
- Vendor lock-in and weak exit clauses leave your organization vulnerable if a provider relationship fails.
- Cyber Advisors delivers expert risk assessments and managed IT services built around your specific compliance requirements.
- Clear SLAs, governance frameworks, and regular vendor audits are essential to reducing outsourcing risk exposure effectively.
Critical Risks to Evaluate Before Outsourcing Managed IT
1. Data Security and Privacy Exposure
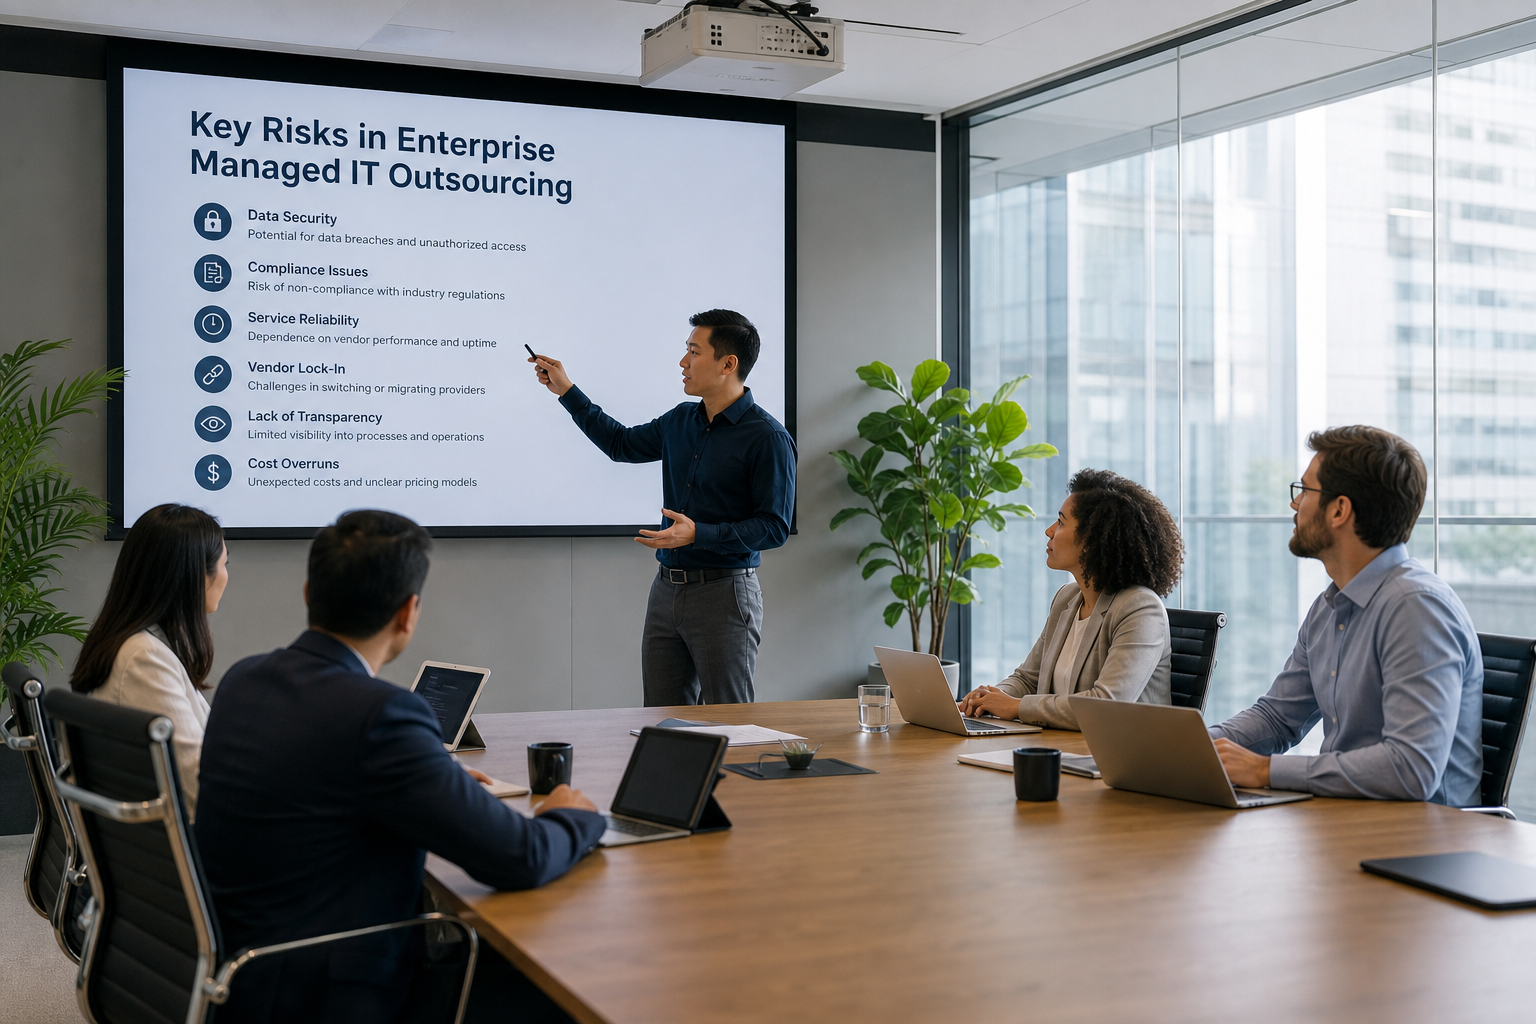
When you grant an external provider access to your infrastructure, every shared login, remote session, and data transfer becomes a potential entry point for attackers. If your vendor's security practices fall short, your customer records, financial data, and intellectual property are at risk.
For regulated organizations, the consequences are compounding. A single misconfigured permission can trigger violations under HIPAA, PCI DSS, or GLBA, resulting in fines, lawsuits, and reputational damage. Demand that your vendor holds current security certifications (ISO 27001, SOC 2) and conduct periodic compliance audits of their environment.
2. Loss of Operational Control and Visibility
Delegating daily IT operations to a third party means your internal teams lose direct oversight of patching schedules, access permissions, and configuration changes. Misaligned priorities between your organization and the vendor can lead to delayed incident responses.
Define clear SLAs and key performance indicators (KPIs) in every contract. According to the 2026 KPMG Global Third-Party Risk Management Survey, only 18% of organizations have fully integrated third-party risk management with enterprise risk management. Governance meetings and real-time dashboards help close that gap.
3. Compliance and Regulatory Risk
Outsourcing does not outsource your compliance obligations. Your organization remains accountable for how data is stored, processed, and protected, regardless of who manages the underlying systems. Vendors operating across different jurisdictions may not understand your industry-specific regulatory requirements.
Non-compliance penalties are steep. GDPR violations can reach up to 4% of annual global turnover, and the SEC now mandates cybersecurity disclosure timelines for financial institutions. Before outsourcing, map your regulatory obligations to specific vendor responsibilities and include compliance clauses, audit rights, and breach notification timelines in every agreement.
4. Vendor Lock-In and Exit Risk
Some outsourcing contracts are designed in ways that make it difficult or expensive to switch providers. Proprietary platforms, custom integrations, and restrictive licensing can trap your organization in a relationship that no longer serves your interests.
Negotiate clear exit provisions from the start. Define data portability requirements, transition timelines, and intellectual property ownership in writing. A well-structured risk management framework should include vendor exit planning as a standard practice, so you can move to a new provider without business disruption.
5. Hidden Costs and Budget Overruns
The initial cost of a managed IT contract often looks attractive, but hidden expenses can accumulate quickly. Change requests, after-hours support, emergency escalations, and licensing fees for additional tools can push your actual spend well beyond the original estimate.
Perform a detailed cost analysis before signing. Require itemized pricing, cap unexpected charges through contractual protections, and build quarterly reviews into your agreement to catch cost drift early.
Monitoring expenses in real time helps you avoid the kind of budget overruns that undermine the financial case for outsourcing.
6. Incident Response Gaps
If a breach or ransomware event hits your environment, your outsourced IT provider becomes the front line of defense. The problem? Not every provider has the expertise, staffing, or playbooks to mount a rapid, effective response under pressure.
Ask detailed questions about your vendor's incident response capabilities before you sign. Do they staff 24/7 security analysts? Do they run tabletop exercises to test their response procedures? If the answer is unclear, that's a signal to look deeper or consider a provider that builds incident readiness into every engagement.
7. Talent and Knowledge Gaps at the Vendor
Your outsourced provider is only as good as the people managing your systems. High staff turnover, reliance on junior technicians, or a lack of specialized skills in areas like cloud security and endpoint protection can erode service quality over time.
During vendor evaluation, ask about technician certifications, retention rates, and how the provider handles knowledge transfer when staff change. A strong provider invests in training, assigns dedicated engineers who understand your environment, and documents institutional knowledge so transitions don't leave gaps in your protection.
8. Communication and Cultural Misalignment
Time zone differences, language barriers, and conflicting work styles can create tension between your team and the outsourced provider. Miscommunication around a critical patch window or an escalation procedure can turn a minor issue into a major outage.
Choose a provider with documented communication protocols, designated account managers, and overlapping business hours. Regular status calls, shared ticketing systems, and transparent risk management reporting help keep both teams aligned. Clear escalation paths ensure that urgent issues reach the right people fast.
How Cyber Advisors Reduces Your Managed IT Outsourcing Risk
Evaluating these risks is a starting point, not the finish line. Cyber Advisors takes a security-first approach to managed IT services, combining 24/7 monitoring, dedicated engineering teams, and proactive threat detection to protect your environment from the vulnerabilities that outsourcing can introduce.
For organizations in healthcare, finance, manufacturing, and government, our risk management and compliance assessments ensure your vendor relationships meet the same standards you hold internally. From penetration testing to adversarial simulation, we test your defenses so you can address weaknesses before they become breaches.
Ready to evaluate the risks in your current IT outsourcing arrangement? Let's take a look together.
FAQs about Key Risks in Enterprise Managed IT Outsourcing
What is the biggest risk of outsourcing managed IT services?
Data security exposure is typically the most significant risk. When a third-party vendor accesses your infrastructure, every shared credential and remote connection becomes a potential attack vector.
Cyber Advisors reduces this risk through layered security controls, encrypted access, and regular vulnerability assessments tailored to your industry.
How can regulated organizations stay compliant when outsourcing IT?
Map every regulatory obligation to a specific vendor responsibility in your contract. Include audit rights, breach notification timelines, and compliance reporting requirements.
Your organization remains accountable regardless of who manages the systems, so oversight and documentation are critical.
What should I look for in an outsourced IT provider's incident response plan?
Confirm that the vendor staffs 24/7 security analysts, maintains documented response runbooks, and runs regular tabletop exercises. Cyber Advisors builds incident readiness into every managed IT engagement.
How do I avoid vendor lock-in with a managed IT provider?
Negotiate data portability, transition timelines, and IP ownership clauses before signing. Clear exit provisions protect your organization if the relationship no longer meets your needs.
Are hidden costs common in managed IT outsourcing contracts?
Yes. Change requests, after-hours support, and licensing fees for additional tools can push costs beyond the original estimate. Require itemized pricing and build quarterly cost reviews into your agreement.
How does Cyber Advisors help enterprises manage outsourcing risks?
Cyber Advisors delivers customized managed IT services with built-in security, compliance auditing, and 24/7 monitoring. Our team works alongside yours to ensure vendor relationships meet your governance and regulatory standards.